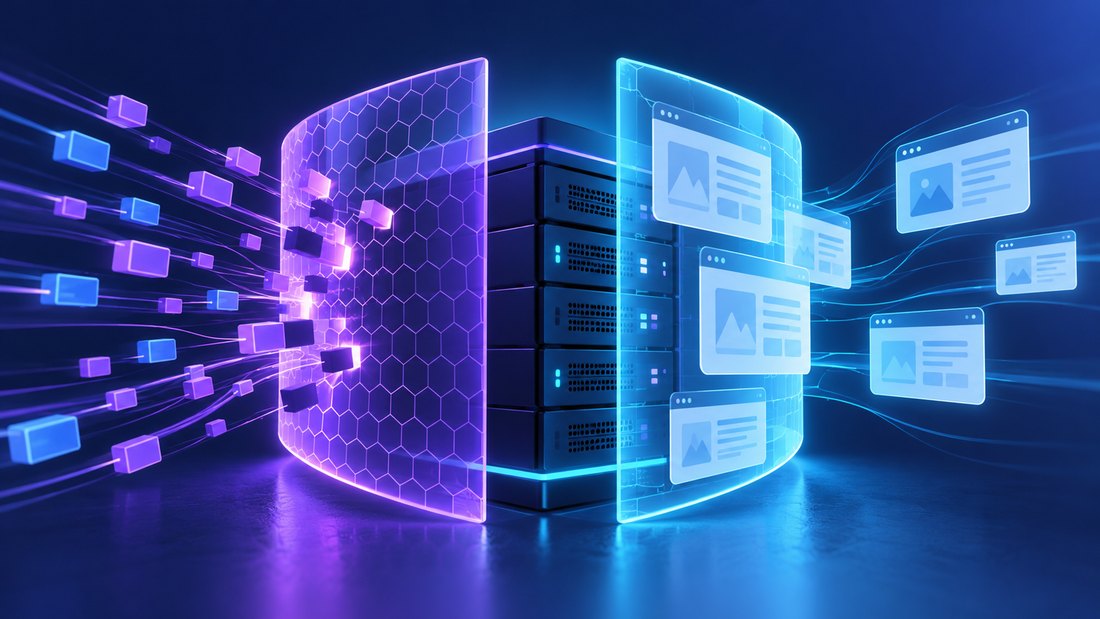
A WAF and a network firewall protect different parts of a website’s path. The distinction matters when a hosting plan advertises a firewall without explaining what it inspects or which traffic passes through it. Buying one type does not automatically provide the controls of the other.
A web application firewall evaluates web requests using application-level information. A network firewall controls network traffic according to the capabilities and rules of that product, commonly including addresses, ports, protocols, and connection state. Some products combine functions, so the correct comparison is their actual coverage rather than their marketing category.
At getaboutcolumbia, the practical question is which unwanted action each layer can prevent. This article explains how the two controls fit together, how to test legitimate workflows, and how to avoid exposing an origin server that bypasses the intended protection.
Match each control to the traffic it can see
Consider a website with public HTTPS, administrative SSH access, and a private database. The public site needs to accept web traffic. SSH should be limited to authorized administration paths, and the database should normally be reachable only by its intended clients. These are network exposure decisions before the contents of a web request are considered.
The AWS security group documentation provides a concrete example: rules specify traffic properties such as source, port, and protocol, and security groups track connection state. The exact rule model differs across hosting platforms. Check both inbound and outbound behavior instead of assuming a rule written for one provider translates directly to another.
A sound set of VPS firewall rules can prevent direct public access to a database port. It will not, by that fact alone, understand whether an allowed HTTPS request contains a malicious form value. Port 443 is still an authorized route to the web application.
Cloudflare’s WAF documentation describes filtering web and API requests using properties such as paths, headers, and body content. This is why a WAF can address suspicious application requests that still arrive through an allowed web port. The supported inspections and rule features depend on the service and plan.
Neither layer proves that the application is secure. A request may be syntactically ordinary yet exploit an authorization mistake, such as one user viewing another user’s order. Application code must enforce its own permissions. Likewise, a valid administrator session can make harmful changes that a generic attack rule cannot reliably distinguish from authorized work.
Draw the actual request path in your operating notes: browser, edge provider, load balancer, origin server, and application. Mark where encryption ends and where inspection happens. This reveals whether a proposed control can see the data it is expected to evaluate and which hops still need their own protection.
Deploy rules with a plan for legitimate traffic
Start by inventorying successful workflows: sign-in, editing, search, checkout, uploads, webhooks, and API clients. A browser challenge may work for a human visitor but fail for a payment notification service. Rate limits can also affect shared networks where many legitimate users appear behind one address.
Use observation or counting modes when the product supports them and the risk allows it. Review which requests would match before enforcing a broad rule. If immediate blocking is necessary, scope the rule narrowly and monitor the affected workflow closely. Keep an owner and a documented rollback for every temporary exception.
A WAF at the edge protects requests that traverse that edge. Cloudflare’s origin protection documentation addresses restricting direct origin access. If the origin remains publicly reachable through another hostname or address, the intended inspection path may be bypassed. Coordinate restrictions with health checks, administration, certificate renewal, and integrations before enforcing them.
Your DDoS protection coverage is another separate question. Filtering a suspicious HTTP request is different from absorbing traffic that saturates the server’s upstream connection. Ask which provider handles each kind of event and where mitigation occurs relative to the resource that can be exhausted.
Test a rule change from the visitor’s perspective and inspect the corresponding security event. Record the rule identifier, matched condition, and observed result. A generic access-denied page without correlation information makes future troubleshooting unnecessarily difficult, especially when the application and edge provider have separate support teams.
When a false positive appears, create the smallest justified exception. Exempting a particular verified callback route can be reasonable; disabling protection for an entire administration area is a much broader decision. Revisit exceptions after an application update, since the reason for the exception may no longer exist.
Mistakes to avoid
Do not assume a host’s included firewall protects every domain, port, or protocol in your account. Some protection applies only to traffic through a proxy or to particular managed services. Ask for the coverage boundary and verify your deployment is inside it.
Avoid changing network and application rules simultaneously during routine maintenance. If access breaks, the source becomes harder to identify. Keep an alternative administrative path and use a website incident response process when emergency changes are required.
Two final recommendations
Maintain a short control inventory with the protected service, rule location, owner, and test method. This makes handover easier and prevents duplicate rules at several layers from becoming an undocumented obstacle to normal operation.
Review denied traffic alongside successful business activity. Fewer requests reaching the origin is not automatically a success if inquiries or orders also disappear. Judge protection by reduced unwanted activity while the required customer workflows continue to function.
Conclusion
A WAF and a network firewall are complementary controls when they are matched to the traffic and risks they can actually address. Network exposure and web request inspection are related but distinct responsibilities.
Map the request path, restrict unnecessary services, deploy application rules carefully, and ensure the origin cannot casually bypass the intended edge protection. Test the workflows that matter after each change.
Choose the controls your architecture needs and your team can maintain. Clear ownership, narrow exceptions, and repeatable checks make those controls more useful than an unspecified firewall feature on a hosting comparison page.