Managing application secrets on a VPS means controlling how passwords, API tokens, signing keys, and other sensitive values reach the software that needs them. The challenge is not merely keeping them out of a public repository. They can also escape through deployment logs, backups, debug pages, process configuration, or overly broad server access.
A small VPS does not automatically require an elaborate secret management platform. It does require a deliberate process for storage, delivery, access, rotation, and recovery. The appropriate mechanism depends on the operating system, application framework, deployment method, and the people who administer the server.
At getaboutcolumbia, this article approaches secrets as operational dependencies. You will learn how to inventory them without exposing their values, choose a delivery method, and rotate a credential without unexpectedly breaking the website or its background jobs.
Inventory secrets and choose a controlled delivery path
List each secret by purpose rather than value: database login, email service token, backup storage credential, payment API key, or session signing key. Record its owner, consumer, scope, storage location, and revocation method. Also note whether production and staging use different credentials and whether a replacement can coexist with the old one.
The OWASP secrets management recommendations describe a lifecycle including creation, rotation, revocation, and expiration. This is a useful framework for a VPS because the hardest failure often appears later: nobody knows which application uses an old key or how to replace it safely.
Keep production values out of source code and reusable application images. Configuration templates can contain variable names and instructions, but should not contain working credentials. If a secret enters a repository, deleting the current file does not revoke copies in history or in other people’s clones. Treat exposure as a rotation problem as well as a cleanup task.
Your least-privilege model should distinguish the runtime identity from people who deploy code and people who administer the host. A process needs only the secrets it uses. A design-only contributor should not receive the backup storage key or the production payment credential. However, anyone allowed to deploy executable code into production can often access secrets available to that runtime. Use restricted staging and reviewed deployment boundaries when that access is not intended.
A restricted configuration file outside the public web directory can be a reasonable mechanism for some small deployments. Its ownership and permissions must allow the intended service to read it while excluding unrelated users. Check whether the web server, backup job, and deployment process can accidentally publish or duplicate it.
Environment variables are convenient, but they are not an automatic secrecy boundary. Debugging tools, process inspection, crash reports, or framework diagnostics may reveal them depending on the environment and privileges. Choose them only with an understanding of those paths, and avoid dumping complete environments into logs during troubleshooting.
Deliver, rotate, and recover without losing control
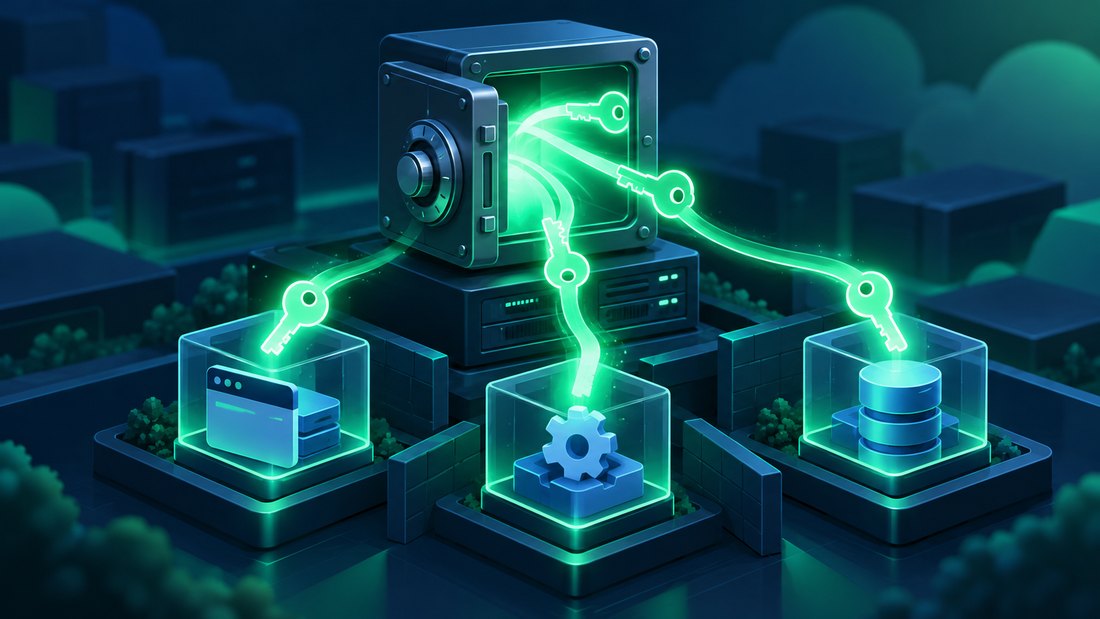
For Compose deployments, Docker’s secrets documentation explains granting a secret to specific services and making it available as a mounted file. This can reduce casual exposure through environment configuration, but the source secret still needs protection on the host. A local Compose secret is not a substitute for securing the VPS itself.
A dedicated secret service may help when several servers or teams need centrally managed access and auditability. It also becomes another dependency to operate. Decide how an application starts during a temporary outage of that service, which identity retrieves the secret, and how emergency access is controlled. Avoid adding a system the team cannot recover.
Plan rotation as a sequence. Create a replacement with appropriate scope, deliver it to the consumer, reload or restart the necessary process, verify a real operation, and revoke the old value once its consumers are accounted for. Some services support overlapping credentials; others require a more carefully coordinated cutover.
Remember background consumers. A website can render correctly while nightly exports, email delivery, or scheduled imports fail with the old credential. Review the complete VPS service configuration and scheduled jobs before declaring rotation complete. The validation should cover the work that normally runs outside a browser request.
Logging deserves explicit checks. The OWASP logging guidance identifies passwords, tokens, connection strings, and encryption keys as information that generally should not be recorded directly. Inspect actual log output from successful and failed operations. Error paths are particularly likely to expose configuration that ordinary requests never print.
Include secrets in disaster recovery planning without distributing them unnecessarily. A restored application may require encryption keys to read stored information or signing keys to preserve expected behavior. Store recovery material securely, document its custodian, and test access in an isolated drill. Losing a key can make otherwise intact data unusable.
If compromise is suspected, do not simply rotate from the affected server and assume the problem is solved. Establish a trusted administrative path, assess what the attacker could read, and coordinate replacement with containment. New credentials delivered into an uncontrolled environment may be exposed immediately.
Mistakes to avoid
Do not use one powerful token for backups, deployments, and every integration. Shared scope makes it harder to revoke a single process and increases the impact of one exposure. Avoid placing secret values in command arguments or support screenshots where they may be retained unexpectedly.
Do not assume an encrypted archive can be shared freely. Anyone with its decryption key receives the secrets inside it. A website backup policy should define who can retrieve archives, how keys are handled, and how restored credentials are reviewed.
Two final recommendations
Create a secret inventory that contains no secret values and keep it current with deployments. Its main purpose is to answer who uses a credential, who owns it, and what must be tested when it changes. That information makes emergency revocation much less disruptive.
Practice rotating a low-impact integration before the critical database or payment credential needs attention. Record the steps and any reload behavior you discover. Use that experience to improve the process rather than relying on memory during an urgent security event.
Conclusion
Managing application secrets on a VPS requires controlled delivery, limited access, predictable rotation, and a recoverable source of truth. The storage mechanism is only one part of the design.
Map consumers, keep values out of code and logs, test credential changes across foreground and background work, and protect the recovery material. Match the tooling to the team’s operating capacity.
Begin with one inventory and one verified rotation procedure. Those two artifacts provide a practical foundation for reducing secret exposure without making routine website operation fragile.