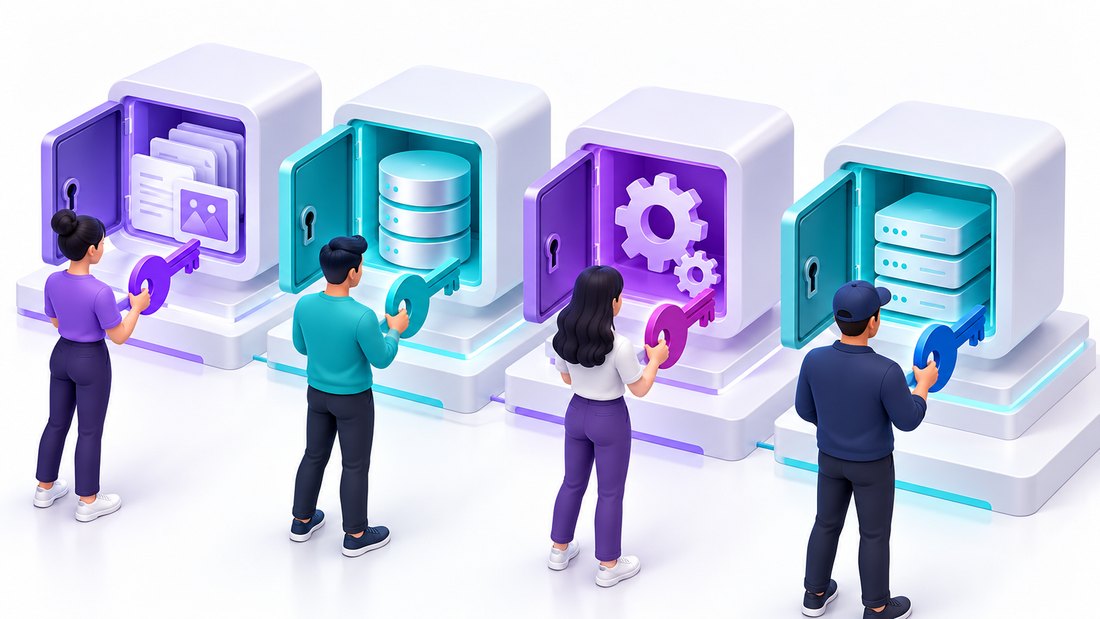
Least privilege for website teams means granting the access needed for a defined task and withholding unrelated powers. Its purpose is practical: a mistaken action, stolen credential, or compromised integration should affect as little of the business as possible. It also makes ownership and offboarding easier to understand.
Permissions exist at several independent layers. A WordPress role, a hosting team role, a Linux account, and a cloud API token do not control the same things. Restricting one layer can leave a much broader route open elsewhere, so the review must follow the work from the application to its underlying infrastructure.
This article from getaboutcolumbia explains how to build an access model for a small website team without making routine work unnecessarily difficult. It covers task definition, permission testing, temporary elevation, and the credentials that are easily overlooked when someone leaves.
Describe tasks before assigning roles
Begin with verbs and resources: edit assigned articles, publish all articles, update a theme, download invoices, restore a database, or change DNS. These descriptions are more useful than job titles. Two developers can need different access if one edits a front-end theme while the other maintains production infrastructure.
The OWASP authorization recommendations emphasize minimum necessary privileges and checking authorization consistently. Apply that principle to your operating process by asking both what a person must do and what they should not be able to do. A role is acceptable only if both sides of that boundary are understood.
Separate ownership from daily administration. The business needs dependable control of its hosting and domain accounts, but ordinary content work should not require those credentials. A secure hosting account arrangement gives named people the access appropriate to their responsibilities while retaining a protected owner identity.
For WordPress, the official roles and capabilities documentation explains how capabilities define permitted actions. Plugins can add or alter capabilities, so test the installed site rather than relying only on the familiar names Editor or Author. A custom commerce role may expose customer information that a publishing-only role does not.
Treat production and staging as separate resources. A contractor who needs to debug a theme may be able to work with sanitized staging data and a deployment handoff. Copying the complete customer database into that environment expands access even if the contractor never receives a production login.
Write a short permission record for each role: task, environment, data exposure, destructive actions, approval owner, and review date. Keep it understandable enough for a nontechnical owner to confirm. If a role combines several responsibilities because the provider offers limited granularity, record that limitation explicitly.
Test permissions and manage their lifecycle
Use a dedicated test identity to verify a new role. Confirm that it can complete its expected workflow and that unrelated actions are denied. Check access through the dashboard and supported API routes where applicable. Hiding a menu item is not the same as preventing the underlying action.
Provider documentation can clarify the intended model. The AWS IAM best practices recommend least-privilege permissions and reviewing unused access. In a smaller hosting panel, the same review may be manual: list members, examine their roles, inspect active integrations, and remove entries with no current owner or purpose.
Machine credentials need their own identities. A backup job that only writes archives should not automatically share the deployment token that can alter servers. Separate credentials make revocation more precise and help identify which process produced an unexpected action. Their supported scope depends on the platform.
For agencies, client ownership and hosting handover should include the permission model. An account created for convenience can become a long-term dependency if only the agency knows how access is delegated. Agree how the client can appoint another operator without rebuilding the entire control chain.
Use temporary elevation for infrequent privileged work when the tools and team can support it. State the purpose, duration, and person approving the change. After the task, remove the extra rights and verify the normal role still works. Emergency access should be available, logged, and reviewed rather than quietly left enabled forever.
Offboarding must follow all access paths. Remove team membership, application users, SSH keys, API tokens, repository access, and credentials the person could retrieve. Some secrets may be shared across services, so plan rotation with the service owner to avoid breaking scheduled backups or deployments.
Review privilege creep after role changes. Someone who moves from billing to technical operations may retain old access unless it is deliberately removed. A recurring review is also useful for inactive service accounts and abandoned plugins, which can remain connected long after their original purpose disappears.
Mistakes to avoid
Do not grant administrator access simply because it fixes an unexplained permission error. Identify the missing capability and determine whether the task truly requires it. Broad access can hide a broken workflow while creating a much larger future exposure.
Avoid treating encryption as permission control. A protected connection still lets an overprivileged account perform an authorized but harmful action. Similarly, application secrets on a VPS require restrictions on who can read them; secure transport alone does not establish that boundary.
Two final recommendations
Start with the highest-impact permissions: changing ownership, deleting resources, downloading customer data, modifying DNS, and restoring production. Clarifying these boundaries first usually produces more benefit than trying to perfect every minor capability at once.
Attach access reviews to real business events. Hiring, contractor completion, role changes, migrations, and new integrations should each trigger a review. A simple checklist used consistently is easier to maintain than an elaborate access matrix that nobody revisits.
Conclusion
Least privilege for website teams is a task-based access discipline across people, applications, infrastructure, and integrations. It reduces the scope of mistakes and makes account control more durable.
Define the work, test what the role permits and denies, separate machine credentials, and remove access when its purpose ends. Keep a controlled path for exceptional administration.
Build the model around the actual team and tools. Useful boundaries that people understand and follow are more effective than restrictive settings that repeatedly force everyone to share the owner account.