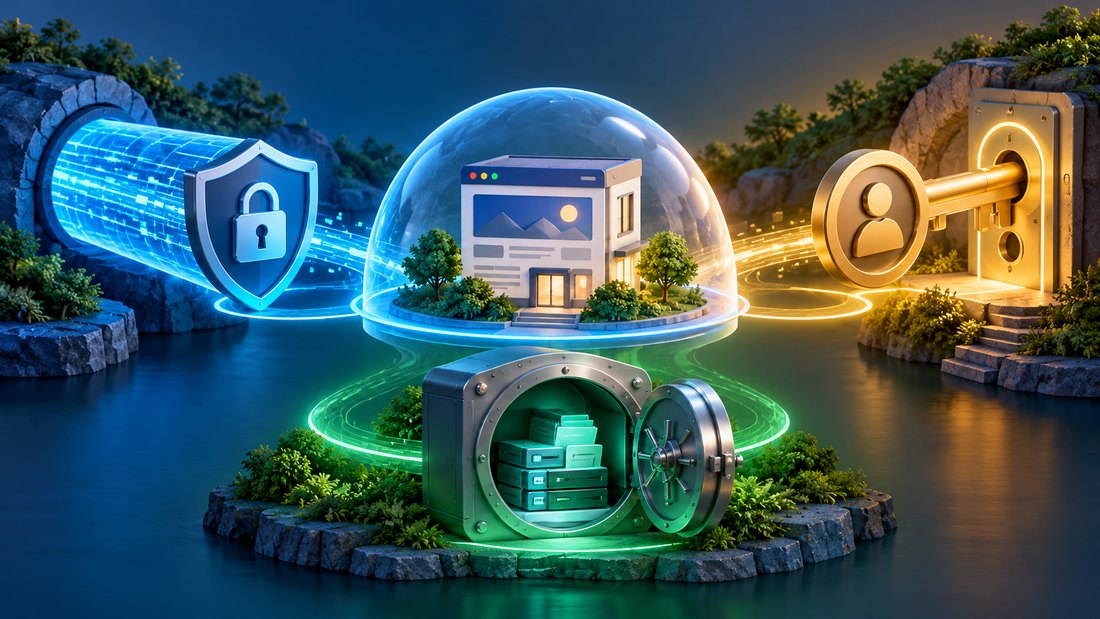
HTTPS, backups, and access controls protect different parts of a website. They are frequently grouped under a hosting plan’s security features, which can make it tempting to treat one visible indicator as proof that everything is protected. A secure connection does not show whether an administrator has excessive permissions or whether deleted data can be recovered.
Each control has a specific purpose and a boundary. HTTPS protects communication using TLS. Backups preserve recovery options for data and application state. Access controls decide who or what may perform actions. All three need correct configuration and ongoing maintenance, and none removes the need to keep the application itself secure.
This getaboutcolumbia article explains those boundaries through practical website scenarios. It also shows how to verify the controls separately so a business owner can ask useful questions instead of relying on a single security badge or a long feature list.
Match the protection to the failure
HTTPS protects the connection between participating endpoints. The MDN TLS explanation describes encryption, integrity, and authentication of the connection. That helps prevent someone on the network from casually reading or changing the protected traffic. It does not certify that the content is accurate or that the website operator is trustworthy.
Consider a visitor submitting a contact form. HTTPS protects the request while it travels through the secured connection. Once the application stores the message, database permissions and server security determine who can read it. If the record is accidentally deleted, recovery depends on backup coverage and retention, not on the certificate used during submission.
Follow the whole connection path. A CDN may terminate the visitor’s TLS connection and create a separate connection to the origin. Verify the security of that origin connection according to the architecture. A certificate renewal process should cover the endpoints the service actually depends on, not just the certificate visible in one browser check.
Backups address a different problem: returning to a recoverable state after loss or unwanted changes. WordPress’s backup documentation distinguishes database and file coverage. For an application, the practical question is whether the saved components fit together and contain the information needed to restore useful functions.
A backup does not prevent an unauthorized person from reading live data. It may also contain sensitive information itself. Store and retrieve archives through controlled access, protect their contents appropriately, and retain the keys needed to restore them. Recovery copies should not become a less protected duplicate of production data.
Access controls decide whether a request or identity may perform an operation. The OWASP authorization guidance emphasizes minimum privileges and consistent permission checks. A user who can sign in should not automatically be allowed to view every account, export every order, or modify the hosting environment.
Verify each control with its own evidence
For HTTPS, inspect the intended domain and relevant subdomains, verify certificate validity and hostname matching, and check that required page resources use protected URLs. Test the actual customer workflow, because a secure homepage does not prove that every embedded resource or redirected destination is configured correctly.
For access, list the roles used by people and integrations. Test whether each can complete its assigned task and whether unrelated actions are denied. Include hosting owner accounts, application administrators, server users, deployment credentials, and backup access. These are separate layers even when the same person operates several of them.
A least-privilege model for website teams makes those checks more concrete. For example, a writer may need to edit content but not install code; a billing contact may need invoices but not DNS control. Record exceptions so broad access does not become permanent merely because it solved a temporary problem.
For backups, run an isolated restoration and compare recovered records with the intended recovery point. Verify files, application configuration, and a controlled business action. A completion message from the backup job is useful evidence that a job ran, but it is not the same as evidence that the resulting service can be rebuilt.
Use scenarios to find gaps between the controls. If a staff account is compromised, which actions can it perform and which historical copies could it delete? If a certificate expires, can the team still access the provider through an independent route? If the server disappears, where are the recovery instructions and credentials?
Assign an owner to each answer. The host may manage certificate issuance while the application team controls redirects and media URLs. A backup provider may preserve data while the site owner remains responsible for testing restoration. Clear responsibilities prevent two parties from each assuming the other verified the missing piece.
Also consider routine changes. A new plugin can add permissions, a media migration can add another TLS endpoint, and an external form service can move valuable data outside existing backups. Review the protection boundaries whenever the website’s data or request path changes.
Mistakes to avoid
Do not describe a website as fully secure because the browser shows an HTTPS indicator. Do not assume a backup cures compromise without removing the entry point and reviewing exposed credentials. Restoration can bring back vulnerable code or unauthorized changes if the recovery point is poorly chosen.
Avoid buying additional tools before confirming the basic controls function. A backup restore drill, an access review, and an endpoint check can reveal specific problems that a general security subscription would not automatically resolve.
Two final recommendations
Keep a brief protection map containing the risk, control, owner, and verification method. It should show how communication, authorization, and recovery are handled without pretending that the three cover every possible application weakness.
Review the map after incidents and major changes. If a failure occurred despite a control being present, identify whether its scope, configuration, or verification was incomplete. Fix that concrete gap instead of simply adding another badge to the hosting feature list.
Conclusion
HTTPS, backups, and access controls serve complementary purposes: protecting communication, preserving recovery options, and limiting permitted actions. One cannot establish that the others are working.
Verify connections, test permissions, and restore representative data in isolation. Follow the website’s actual endpoints and data stores, and assign responsibility for each protection boundary.
Treat security as a set of observable operating practices. A business owner who understands what each control protects can make better decisions and recognize missing coverage before it becomes a costly incident.